GPS Interview
Timothy H. Edgar
Professor of the Practice of Computer Science, Brown University, and Lecturer on Law, Harvard Law School
MPA 2027, Brown University · November 9, 2026
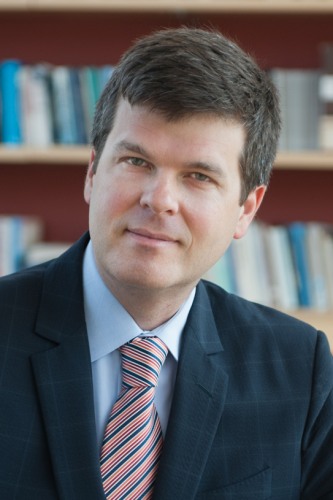
Timothy H. Edgar is a leading expert on cybersecurity and privacy, with over two decades of experience as a scholar, national security official, and privacy and civil liberties lawyer. He is a professor of the practice of computer science at Brown University, a senior fellow at the Watson School of International and Public Affairs, and helped launch Brown’s cybersecurity master’s degree program. He also teaches a course in the legal problems of cybersecurity at Harvard Law School, where he is a lecturer on law. Timothy had previously served in the intelligence community at the Office of the Director of National Intelligence, which included a detail at the White House (2009-2010) as the first-ever privacy official for the national security staff in a position created by President Barack Obama. He recounts these experiences in his book, Beyond Snowden: Privacy, Mass Surveillance and the Struggle to Reform the NSA, winner of the 2018 Chicago-Kent College of Law/Roy C. Palmer Civil Liberties Prize. Prior to his government service, Timothy served as a legislative counsel for the ACLU, which he joined in 2001 shortly before the 9/11 terrorist attacks. He was a law clerk to Judge Sandra Lynch of the United States Court of Appeals for the First Circuit, and is a graduate of Harvard Law School (1997) and Dartmouth College (1994).
Edgar spoke with MPA students at Brown University’s Watson School on November 9, 2026. The conversation has been edited and condensed for clarity.
Q1 Our presentation looked at biometrics, bot detection, and online voting, all of which promise to improve some aspect of election security or accessibility but also introduce new risks. What principle do you think policymakers should use to determine when adding new technology actually makes an election more secure rather than simply creating a different set of vulnerabilities?
I think you need to ask the technical computer science community what kinds of vulnerabilities we’re talking about and whether the technologies being proposed can address them. Voting systems have very specific security requirements, and there has been a consensus in the technical community for many years that the internet is not a secure environment in which to vote… Voting is a unique problem. Only an eligible voter should be able to cast a vote, that vote should not be alterable, and it should not be possible to link the vote back to the voter. Those requirements are very difficult to satisfy online. Verified Voting, an organization I’ve been involved with for many years, has taken the position that internet voting does not work at scale… Even the International Association for Cryptologic Research, which includes some of the world’s top cryptographers, had to rerun an election after its cryptographically secure voting system broke down. That might work for a small organization, but it would not work for a large-scale national election. A physical paper ballot makes a major difference because it allows the counting of votes to be audited in a way that a purely electronic ballot cannot. Technologies like facial recognition also raise reliability concerns at scale, including differences in accuracy across populations and over time. I understand why internet voting is intriguing. It could be more convenient and potentially increase participation, but it is not ready for prime time.
Q2What are currently the biggest points of failure in securing the confidentiality, integrity, and authenticity of electronic voting systems, and are these weaknesses realistically manageable enough for electronic voting to be implemented nationally in the foreseeable future?
The answer is flat out no. We’re not going to be able to implement electronic voting on a national scale anytime soon, and probably ever. There are many potential points of failure, including the software itself. Even if the underlying cryptography is secure, you still have to trust the software running on each machine and the network connecting those machines and counting the votes. That doesn’t mean machines cannot be used in election administration or vote counting. They absolutely can, but you need some form of ground truth, and the way to do that is through a paper ballot. Machines can help voters mark ballots and can read and count them, but if something goes wrong, you still have a human-readable record. In Rhode Island and many other states, we use risk-limiting audits, where a subset of paper ballots is hand-counted and compared with the reported result. If the results fall outside an acceptable margin, more ballots are counted until we establish ground truth. You cannot do that with ballots cast remotely without a paper record.
Q3Based on your experience at the White House, what do you think is the biggest challenge in getting intelligence agencies, election officials, and technology companies to work together effectively without compromising civil liberties?
Public perception is very important when it comes to foreign interference in elections. During the first Trump administration, the intelligence community tried to educate the public about foreign threats to the electoral process. But because those efforts became linked to the legitimacy of Trump’s 2016 election and later claims about a rigged 2020 election, they became perceived as partisan… I don’t think those efforts were partisan. The intelligence community was trying to explain what it was seeing from foreign adversaries, particularly Russia and, more recently, China. But the perception of partisanship made those efforts less effective and potentially damaged the intelligence community’s reputation as a source of neutral and independent information. It is also very difficult to measure the effect of foreign propaganda in a large-scale election. Our information environment is shaped by many factors, including our own behavior and interactions with online platforms, making it difficult to isolate the effect of foreign actors. I think it will take years to determine how the intelligence community can provide useful information about election interference while maintaining public trust.
Q4When researchers find a real security flaw in voting technology, how should organizations like Verified Voting decide how much to warn the public, knowing that those findings could also be used to cast doubt on a valid election result?
There is a big difference between identifying a vulnerability in an election system and having evidence that the vulnerability was actually exploited. The fact that a vulnerability exists does not mean it was taken advantage of… Researchers need to identify flaws in voting machines so those problems can be patched. Inevitably, someone may use the existence of those vulnerabilities to cast doubt on the legitimacy of an election. But saying that a system could be hacked and saying that it actually was hacked in a way that changed an election outcome are completely different claims. If someone believes an election was actually subverted, that claim should be tested through an adversarial process in court, where evidence must be presented and challenged, or at minimum through academic peer review. If you make a claim that an election was hacked but are unwilling to subject it to either of those processes, I think it is reasonable to dismiss it.
Q5If AI begins to be incorporated into vote-counting technology, would you see it as an opportunity to improve efficiency and accuracy, or would it create additional concerns about election security, transparency, and public trust?
I would say absolutely not. AI is not an accurate method for counting, and it would be a disaster to rely on it for vote counting. AI has a lot of interesting potential, but counting is a basic computing process. You don’t need AI to do it… What you do need is a real appreciation for the security requirements of an election system. I don’t think we’ll ever use AI to count votes.
Q6Given the threat of cyberattacks and election interference from foreign countries, what role do you think international cooperation and diplomacy can play in strengthening election security and protecting democratic institutions?
We already have a decent amount of international cooperation on cybersecurity among countries concerned about these kinds of attacks. An attack on another country’s election process is a direct attack on its sovereignty and violates the basic norm of non-interference… International law distinguishes this kind of activity from espionage and intelligence gathering, which have long been part of international relations. Malicious cyber activity may be used for espionage and intelligence collection, but using it to interfere with another country’s political process is an attack on that country’s sovereignty…Those principles and standards are important, but deciding what to do when they are violated is much more difficult. A lot depends on cooperation among close allies, particularly through intelligence and law-enforcement relationships.